There I was, ending my long day as a penetration tester and thinking maybe it was time to retire my Mazda CX-5, when it hit me. I want a sports car. Since I was young I’ve always wanted a Porsche. That way my parents would finally be proud of me.
I decided I’m going to buy a Porsche! Then I found myself staring at an empty bank account. Money has never been a good motivator for me, but a solid goal gets me going. So it was time to get back into bug bounties. The goal was simple: spend a year getting back into the bug hunting grind and try to get myself a Porsche.
When I started in December 2025, the Porsche I was looking for (a 718 Cayman GTS 4.0) was going for around $90k. To make the goal more reachable, I’d put the money from selling my Mazda toward it, roughly $15-20k.
So about $70k. That’s a lot of bounties.
Bright-Eyed and Naive
My first run at bug bounty was back in 2019, during my second year as a pentester. I figured it couldn’t be that different. It was. The learning curve is sharp in ways you don’t expect coming from pentesting.
I did get lucky early, though. During my first month I was going down every possible path on a target and noticed something strange about the password reset. It didn’t send you a reset link. It generated a new password for you, and that password was based on the time.
So if I reset my own account and a victim’s account at exactly the same minute, the new password I got gave away 4 of the 8 characters of theirs. That left 4 characters to guess, and nothing stopped me from guessing as many times as I wanted.
Account takeover.
I proved it out on my test accounts and submitted it. Then came triage. (If you’re new to bug bounty: triagers review your report before the company sees it, and they decide whether it’s valid and how severe it is.)
The triager wanted proof on an account they controlled, so they set one up and asked me to guess its password. The catch: the 4 characters I didn’t know were hex, which meant up to about 65,000 guesses, and the program’s rules said no brute forcing. So, naively, I pointed out that this would break the ToS. Here’s how that went:
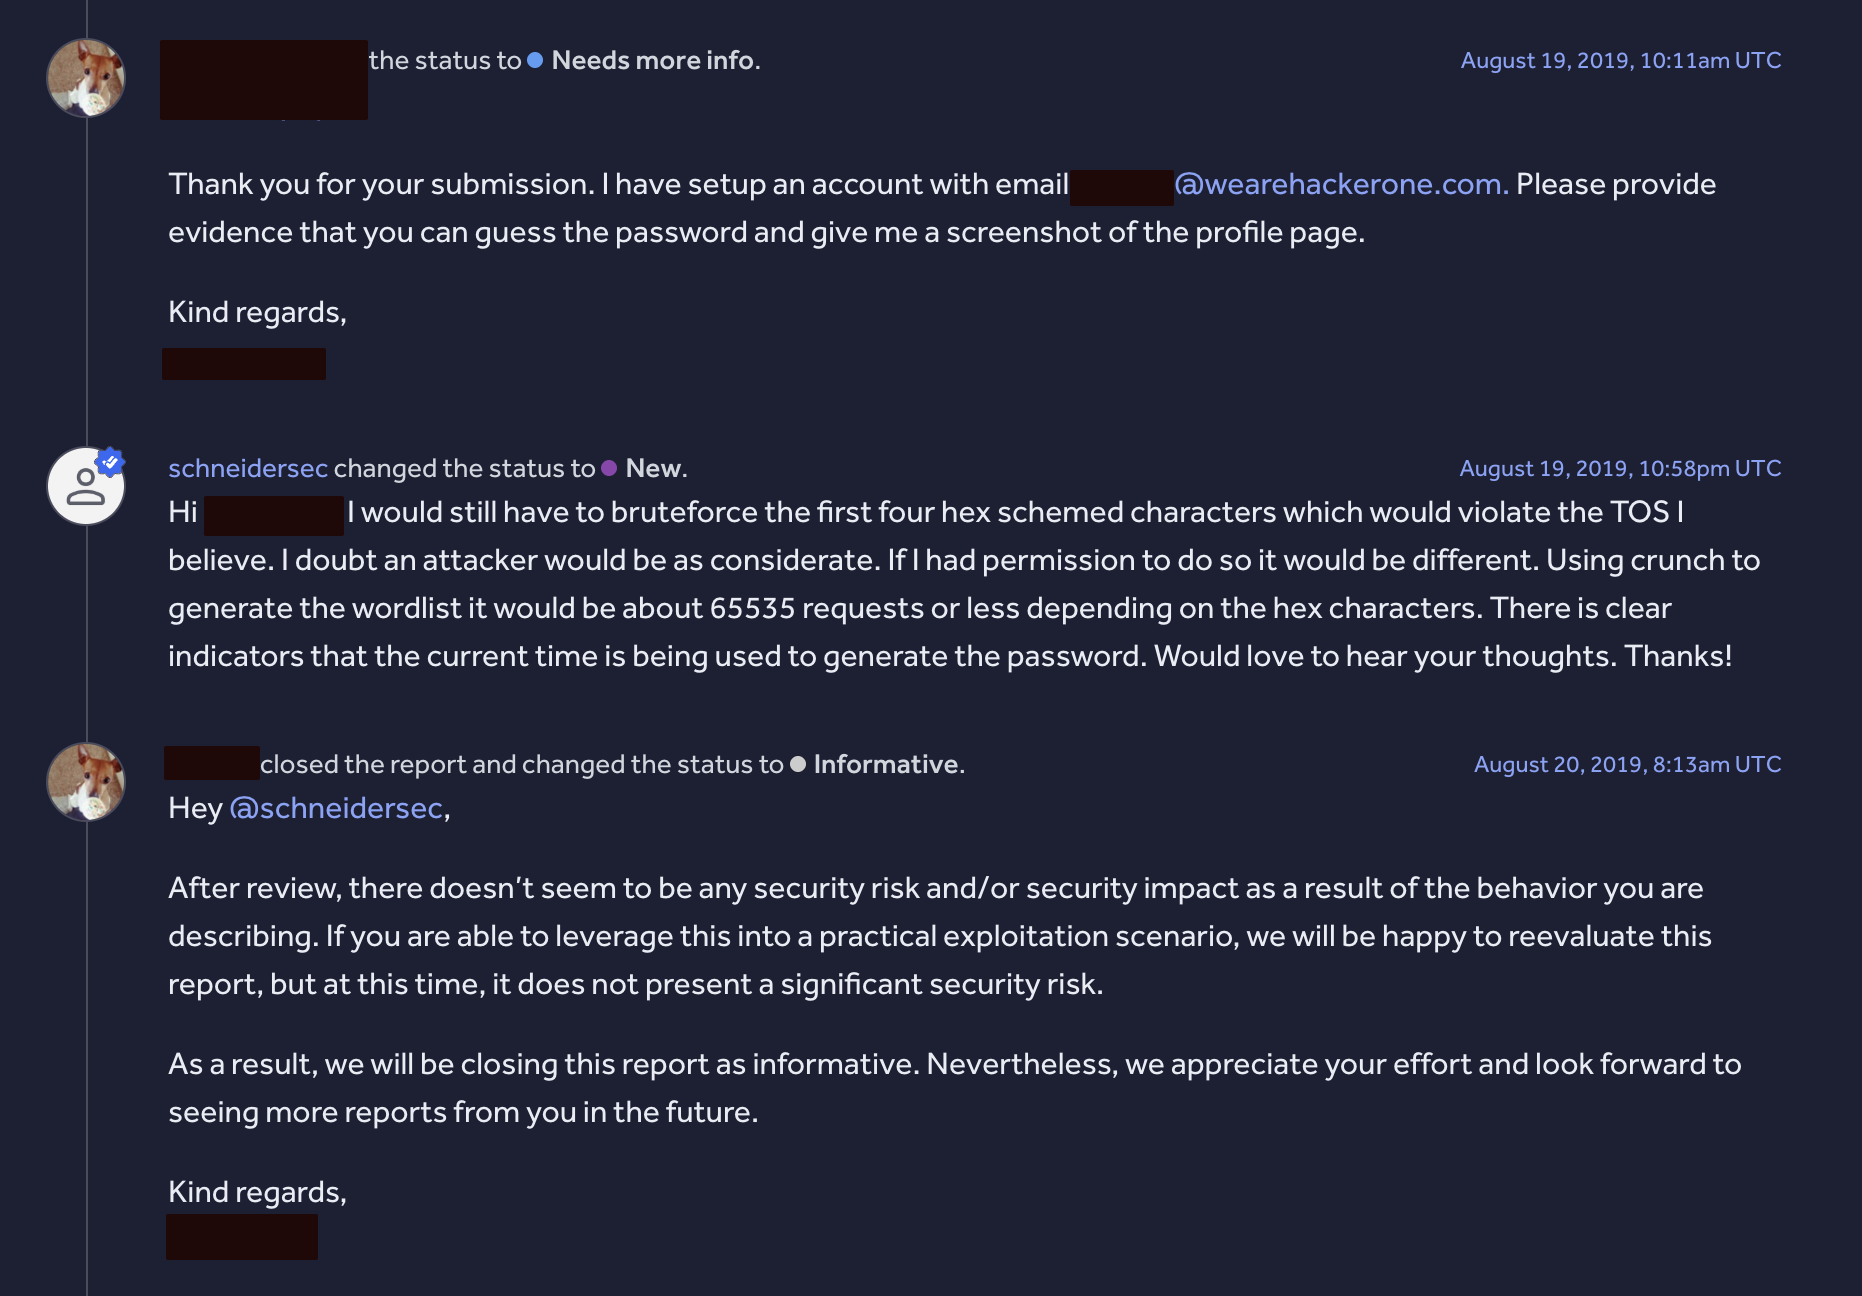
Translation: Nice try sport, you’ll get it next time.
Woah woah woah. Okay. I’ll play ball.
Twelve days later, about 7,000 requests in, I had their password:

The report went from informative to high, and the bug was confirmed on September 3rd. Then nothing. Over a month later, I had to go ask when the bounty would actually be awarded:
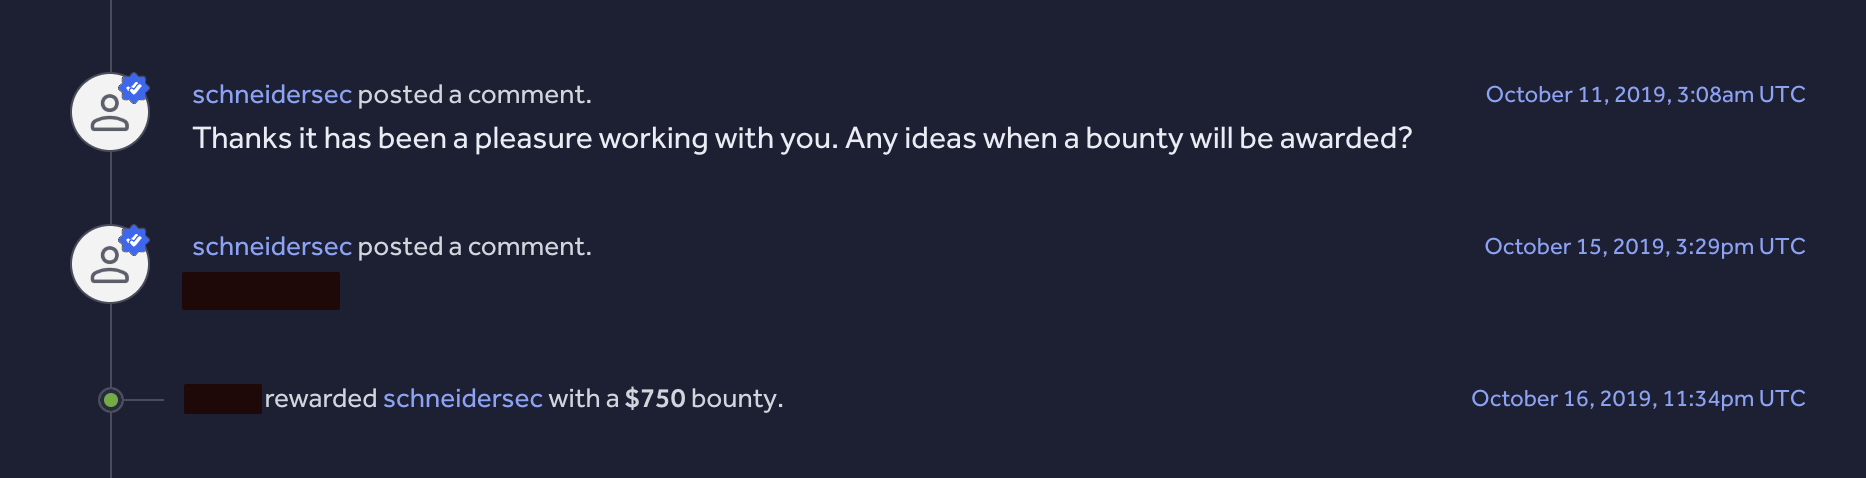
From submission on August 17th to payout on October 16th: two months, for $750. Yikes!
But I was young, didn’t care, and was just happy to have found a vulnerability that paid me.
Lesson learned: impact, impact, impact!
Don’t Call It a Comeback
After that first run, I went back to focusing on pentesting. Then six years went by.
When the Porsche idea pulled me back in December 2025, I didn’t want to just pick up where I left off. A lot had changed. I wanted to use AI, not only to help me build tools but to help me actually find vulnerabilities. And instead of running scans from one machine, I could spin up a fleet of cloud servers with tools like Axiom and get through them much faster.
Ten months in, I’ve learned a lot, from new techniques to mindset and reporting. I’ve also figured out what kind of hunting I actually want to do. I’ve found a good amount of vulnerabilities and made some money along the way. And I’ve spent a lot of time building tools.
This post is the map. Everything I’ve built and learned gets its own post, so pick where you want to start.